Capture
Ingest the consequential decision through REST, Python/TypeScript SDKs, OpenTelemetry/OTLP or MCP.
Capture the agent, delegated authority, model and policy context, human approval, external action and observed outcome — then seal them as portable evidence whose integrity and provenance can be verified independently.
 Inception
 for Startups
 for Startups
Preserve accountability, not only telemetry.
Keep n8n, Zapier, LangGraph or your own runtime.
Incident, customer, audit and regulatory workflows can use the same underlying record.
Export the record and verify it outside the LoopGrid UI.
LoopGrid brings together identity, delegated authority, model context, policy, human oversight, external action and observed outcome in one append-only signed record — then makes that record independently verifiable.
Animated diagram. Evidence from systems around a synthetic refund decision flows into a LoopGrid decision envelope. The append-only record is signed, then independently verified by an auditor, security team, customer and CI pipeline.
Evidence around the decision
— — — —0 of 7 capturedWho can verify it
Want to inspect real signatures and test a mock business action? Open the synthetic evidence lab →
A $720 refund crosses a human-approval threshold. LoopGrid captures the accountable steps as they happen — who proposed it, which policy applied, who approved it, what tool ran and what outcome actually occurred.
“I was charged twice. Refund the duplicate $720.”
support-agent-04 · refund:create · delegated limit $1,000
refund-policy v17.3 · human approval required above $500
Alice reviews the $720 refund and approves the proposed action
stripe.refunds.create is called after the approval event
Stripe reports the refund succeeded · re_demo_720
All required evidence is present and the signed record verifies
The evidence model is append-only. Reviews, actions, outcomes and replays become new signed events instead of rewriting the original decision.
Ingest the consequential decision through REST, Python/TypeScript SDKs, OpenTelemetry/OTLP or MCP.
Commit each evidence event to a workspace-isolated hash chain and sign it with the configured LoopGrid signer.
Reconstruct what happened, inspect approvals and policy versions, and run counterfactual replay without mutating production history.
Export a portable evidence bundle and verify hashes, signatures and chain continuity offline with signer pinning.
Which agent, service version and deployment acted.
Who it acted for, with which scopes and limits.
Provider, model and relevant prompt/context provenance.
The exact policy ID and version evaluated at decision time.
Approvals, rejections and adjudications become signed history.
The state-changing tool or operation the system executed.
What the external system actually reports happened.
Content commitment, chain link, signer identity and checkpoint evidence.
Investigate decisions, policy lineage, human oversight, actions and outcomes from one evidence workspace — then hand the record to someone else to verify independently.
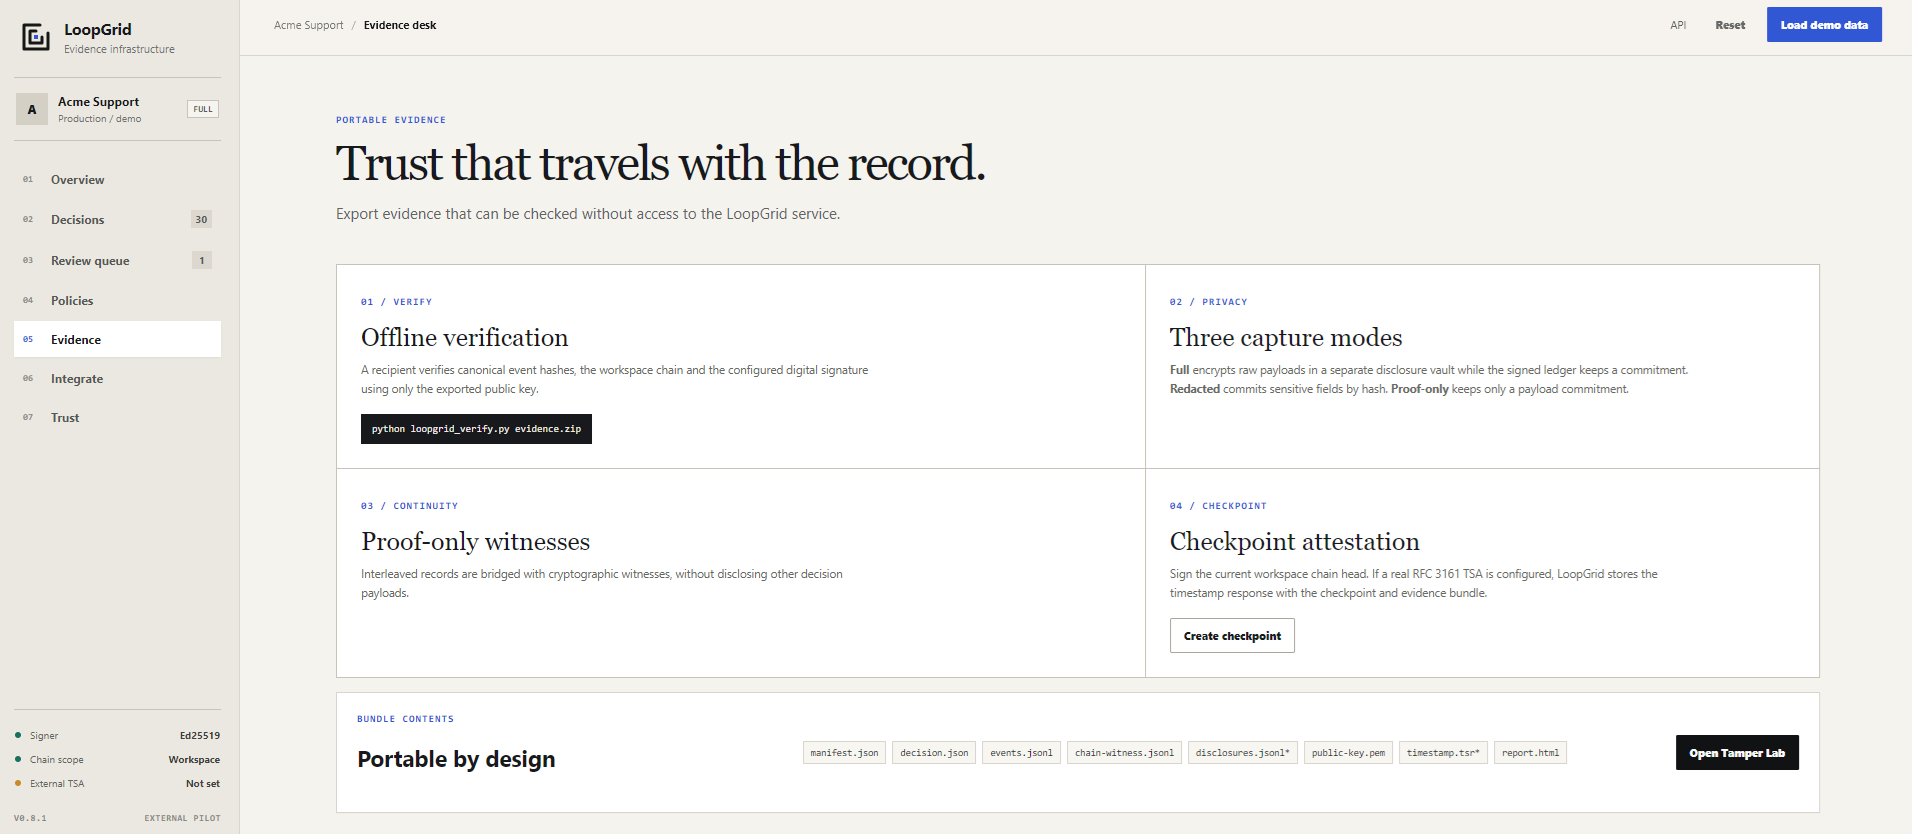
A customer, security team or investigator can receive an evidence bundle and independently verify it. The bundle can include disclosures or withhold them while preserving the signed commitment.
Native integrations for the platforms your agents already run on, plus SDKs and open protocols for everything else. Every path writes the same LoopGrid evidence model.
 DifyVerified marketplace plugin
 n8nVerified node on n8n Cloud
 LangflowSix components on PyPI
 Strands AgentsNative plugin · PyPI
 Google ADKNative BasePlugin · PyPI
AgnoNative hooks · PyPI
 JevTyped decisions via Vercel AI Gateway
 OpenAIModel context capture
 AnthropicModel context capture
 OpenTelemetryOTLP/HTTP protobuf + JSON
 MCPProxy + registry server
 GitHub ActionsVerify evidence in CI
Also available through REST, Python and TypeScript SDKs, OTLP/HTTP and independent verification.
View all integrations →Product names and marks belong to their respective owners and indicate compatibility or integration only; they do not imply partnership or endorsement.
LoopGrid separates signed evidence from raw disclosures, so teams can choose how much data to retain while preserving the cryptographic commitment.
Raw payload can live in a separate AES-256-GCM vault while the ledger retains its cryptographic commitment.
Configured sensitive values become typed/hash commitments while the surrounding evidence remains readable.
Store only the commitment and evidence metadata. Original sensitive data can stay in the customer's environment.
Out-of-band capture is the low-friction default. When the evidence claim depends on whether a tool actually changed external state, use the MCP / action / outcome path so the record can include what the downstream system reports happened — not only the agent's assertion.
The strongest first workflows are not generic chatbots. They are agents that move money, change records, create permissions, communicate with customers or invoke tools that alter real system state.
Preserve which AI system influenced a workflow, the policy/context at the time, human oversight and the resulting action or outcome.
Explore mortgage & credit →Preserve authority, threshold policy, approval lineage, external action and the outcome reported by the downstream system.
Explore financial & risk →Preserve delegated authority, rules, human intervention and the state change that followed.
Explore enterprise agents →Connect the conversation to identity/authorization, policy, tool execution and the system-confirmed outcome without replacing native call logs.
Explore voice & customer ops →We will instrument the evidence path, run a real scenario, verify the evidence independently and define what a production deployment would require in your environment.
Bring a production or pilot workflow. We will map the evidence path, capture the decision lifecycle and show what a hardened deployment would require in your environment.
No. LoopGrid can ingest observability signals, but its primary job is to preserve decision accountability as portable evidence: identity, authority, policy, oversight, action, outcome and cryptographic proof.
No. Workflow runtimes execute the process; observability and control products explain or govern it. LoopGrid is designed to sit alongside them and preserve the evidence of the consequential decision.
No. Evidence integrity can support governance, audit and regulatory workflows, but it is not by itself a legal compliance determination.
No. FULL, REDACTED and PROOF-ONLY modes let a team store encrypted disclosures, hashed field commitments or only the cryptographic commitment.
Yes. Portable evidence bundles can be verified offline, and signer pinning lets a recipient verify the signer against an out-of-band trusted identity.
v0.8.1 is the current Design Partner patch release. PostgreSQL/Docker persistence, restart recovery, signing-key persistence, chain continuity and OTLP/HTTP protobuf + JSON ingestion are validated on the current baseline. Deployment-specific controls such as managed signing, timestamp trust and scaling are reviewed with each environment. See the Security page for the technical readiness matrix and threat model.